


Streamlining POA&M Management in Your CMMC Compliance Software Dashboard
Learn how to streamline POA&M management using CMMC compliance software dashboards. Track remediation milestones and secure your NIST 800-171 posture.
For contractors operating within the Defense Industrial Base (DIB), navigating Department of Defense (DoD) cybersecurity regulations requires constant vigilance. As organizations work toward achieving full alignment with NIST SP 800-171 and CMMC standards, it is rare for any company to achieve a 100% implementation score right out of the gate.
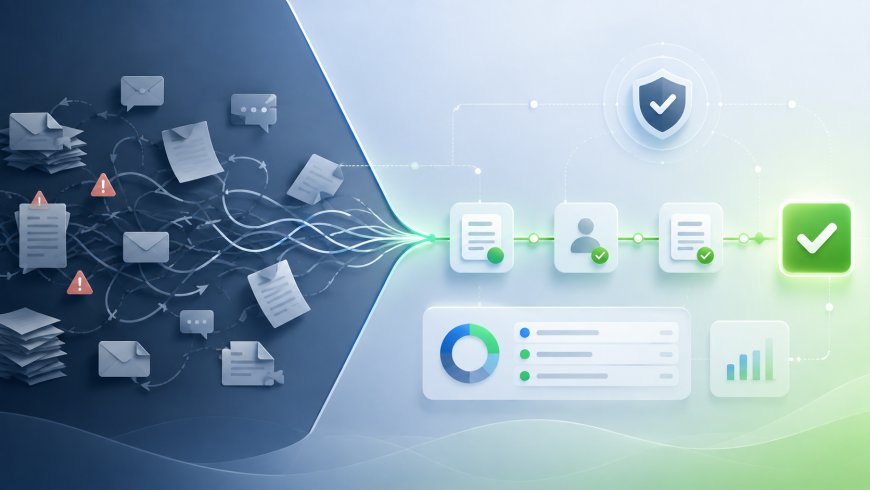
When security gaps exist, the DoD requires a formal roadmap to track how and when those vulnerabilities will be resolved. This master roadmap is known as the Plan of Action and Milestones (POA&M). Managing these milestones manually through scattered spreadsheets can quickly become an administrative nightmare. Today, defense contractors are shifting toward modern solutions, utilizing advanced cmmc compliance software dashboards to master poa&m management and streamline their path to audit readiness.
The Role of POA&Ms in CMMC and NIST 800-171 Compliance
Under the NIST SP 800-171 framework, a POA&M acts as an official tracking document for any security requirements that have not yet been fully implemented. Instead of failing an assessment outright for missing controls, organizations can document their remediation plans, showing assessors the exact steps, resources, and timelines dedicated to closing the gap.
However, managing a POA&M comes with strict rules and high stakes:
-
The CMMC Rulebook: Under current CMMC guidelines, certain critical security requirements (often high-weight 5-point controls) are restricted and cannot indefinitely reside on a POA&M. You must resolve them before your formal assessment.
-
Audit Scrutiny: When a Certified Third-Party Assessor Organization (C3PAO) reviews your environment, every single item on your POA&M will be scrutinized. Vague descriptions, missed deadlines, or unassigned responsibilities will trigger immediate audit failures.
The Pitfalls of Managing POA&Ms Manually
Many small and mid-sized defense contractors attempt to manage their POA&Ms using traditional spreadsheets or static documents. This approach creates significant operational vulnerabilities:
-
Version Control Chaos: As IT teams fix bugs, update configurations, or adjust timelines, static spreadsheets quickly fall out of sync. Assessors can easily spot discrepancies between what is written on a spreadsheet and what is happening on the network.
-
Lack of Real-Time Accountability: Spreadsheets do not send automated alerts when a remediation milestone is approaching or overdue, leading to dropped tasks and non-compliance.
-
Disconnected Documentation: A POA&M cannot exist in a vacuum; it must tie directly into your master System Security Plan (SSP) and your current sprs score calculator metrics. Spreadsheets make this cross-referencing tedious and prone to human error.
Streamlining Remediation via Compliance Dashboards
Modern nist 800 171 compliance software replaces manual tracking sheets with centralized, intuitive dashboards designed specifically for automated poa&m management.
1. Centralized Milestone Tracking
A dedicated compliance dashboard brings all your unmitigated controls into a single pane of glass. You can assign owners to specific tasks, set strict target completion dates, and log evidence of remediation as work is completed. This keeps internal IT teams accountable and provides a clear audit trail for external assessors.
2. Automated Gap Assessment Integration
Before you can manage a POA&M, you must accurately identify your vulnerabilities. Utilizing an automated cmmc gap assessment tool within your software platform automatically populates your POA&M based on active scan results and control deficiencies, eliminating manual data entry errors.
3. Real-Time Synchronization with Your SSP and SPRS Score
As your team closes out a milestone and implements a security control, the platform should automatically update your master documents. Using an integrated System Security Plan (SSP) generator, your system documentation updates in real-time, while your calculated sprs score dynamically increases to reflect your improved security posture. Furthermore, ensuring your entire compliance dashboard operates within a FedRAMP authorized compliance platform guarantees that your sensitive remediation data remains fully protected under rigorous federal standards.
Conclusion
Managing a Plan of Action and Milestones doesn't have to be a chaotic administrative burden. For defense contractors striving to protect their supply chain status, relying on static spreadsheets introduces unnecessary risk and audit exposure.
By leveraging specialized nist compliance software with built-in dashboard capabilities, organizations can take control of their remediation workflows, streamline poa&m management, and ensure continuous, verifiable readiness for their CMMC assessments.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0